~/sacred-heart/cybersecurity$whoami

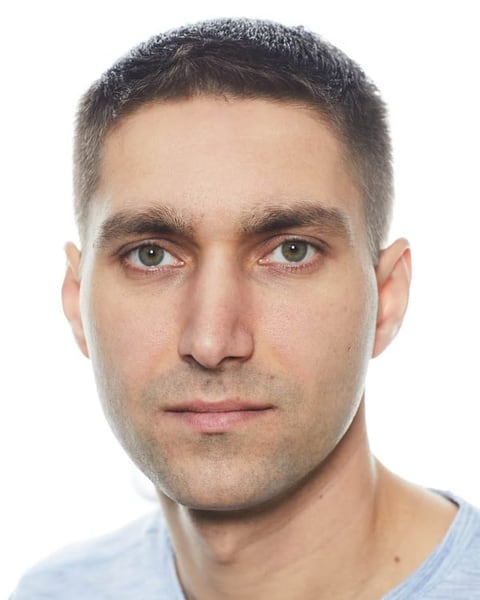
Igor Khokhlov

Assistant Professor of CybersecuritySchool of Computing & Engineering, Sacred Heart University

ResearchingResearching: AI for cybersecurity, metadata-resistant messaging, data quality and IoT security, Android collusion detection, explainable email defense

I am an Assistant Professor of Cybersecurity at Sacred Heart University. My research connects artificial intelligence, data quality, mobile and IoT security, and privacy-preserving communication. I teach undergraduate and graduate computing and cybersecurity courses, with an emphasis on practical exercises, secure system design, and evidence-based security decisions.

Igor Khokhlov
Dr. Igor KhokhlovCybersecurity facultySacred Heart University
  • 34publications
  • 26conference papers
  • 5journal articles
  • 4courses this fall

Teaching

Courses I am teaching in Fall 2026.

Teaching portfolio and mentoring

  • CY-212 / ITI-212

    Web Development in UNIX

    Undergraduate, Fall 2026

    Students build accessible, responsive web applications with HTML, CSS, JavaScript, server-side code, SQL, Git and UNIX workflows. Security is part of the build from the start: forms, authentication, sessions, database access and deployment are all done with secure practices.

  • CY-221

    Foundations of Cybersecurity

    Undergraduate, Fall 2026

    An introduction to security principles, assets, threats, risk, human factors, identity and incident response. Practical cases train students to explain security decisions to both technical and nontechnical audiences.

  • CY-410

    Software and System Security

    Undergraduate, Fall 2026

    Brings together threat modeling, secure architecture, identity and access control, vulnerability management, cryptography, monitoring, incident response, and software and mobile security. Students apply them in hands-on labs and a final project.

  • CY-424

    Emerging Trends in Cybersecurity

    Undergraduate, Fall 2026

    Examines AI both as a defensive tool and as an attack surface. Topics include adversarial machine learning, security of LLM applications, risks of retrieval-augmented generation and agents, software supply chains, cloud identity, post-quantum migration and critical infrastructure.

Selected publications

Six papers that represent the main lines of my research. The full list is organized by year and type.

All publications

Research

Each theme below lists the question, the method, what has come out of it so far and where it stands.

Published 2026, with simulation artifacts

Privacy and metadata-resistant communication

G.H.O.S.T. studies how graph-based routing and decoy traffic can obscure message recipients. The research models privacy through entropy and examines the communication overhead and token incentives associated with different routing choices. The public repository contains simulation code and results accompanying the ICISSP 2026 paper.

Question, method and outputs
Question
How well can decoy traffic keep an observer of the network from learning who a message was for, and what does that cost in bandwidth and incentives?
Method
Simulations of decoy routing trees with varying depth and branching; Shannon entropy of the apparent recipient set; an intersection-attack experiment; modeled latency, saturation and token balances.
Outputs
Peer-reviewed conference paper (ICISSP 2026) and public simulation code with CSV results. Latency figures come from models, not from a deployed network.
Published 2022–2023; ongoing

AI and machine learning for cybersecurity

This work runs in two directions: using machine learning to detect and characterize threats, and studying the threats that AI-enabled systems themselves face.

Question, method and outputs
Question
How far can automated analysis take over vulnerability curation from human analysts, and how robust are ML systems when their data or models are attacked or degraded?
Method
LSTM models combined with expert systems for extracting software names from vulnerability reports; empirical validation against curated data; anomaly detection; a framework cataloguing attacks, defenses and tools for AI/ML systems.
Outputs
Journal article in IEEE Transactions on Software Engineering (2023), conference papers, and an arXiv preprint (2022). LLM and agent security is currently part of the CY-424 curriculum rather than a separate research project.
Published 2017–2024

Data quality and security in mobile and IoT systems

I investigate how data quality and security can be evaluated together in mobile and IoT systems. This work develops evaluation frameworks and sensor-selection methods that account for both the usefulness of data and the security of the systems that produce it.

Question, method and outputs
Question
When a system selects or combines sensor data, how should accuracy, reliability and the security of each source be weighed against each other?
Method
Integral evaluation frameworks for smartphones, a knowledge base and knowledge graph of mobile sensors, genetic algorithms for sensor selection, and adaptive data fusion.
Outputs
Journal articles in ACM JDIQ (2024), IEEE Systems Journal (2021) and IEEE Sensors Letters (2020), the doctoral dissertation, and a series of IEEE Sensors and WF-IoT papers.
Published 2017–2020

Mobile and Android security

Collusion attacks happen when two or more apps coordinate, each staying within its own permissions, so that together they get around the boundaries that are supposed to keep them apart. This work detects that coordination and evaluates the security of Android devices.

Question, method and outputs
Question
Can coordinated behavior between apps be recognized from what the operating system observes while they run?
Method
Monitoring and processing of system signals, anomaly detection with machine learning, recurrent neural networks, and D.I.F.E.N.S.E., a distributed framework for Android security evaluation.
Outputs
Conference papers at IJCNN, ICMLA, the IEEE DASC/CyberSciTech congress and FRUCT, among others.
Work in progress

Business email compromise and explainable AI

Ongoing work explores hybrid and explainable AI approaches to business email compromise detection, with attention to social engineering, message context, and explanations that help people evaluate alerts.

Question, method and outputs
Question
Can a detector catch business email compromise and also explain its reasoning well enough for a person to decide what to do with the alert?
Method
A hybrid of natural language processing, machine learning and rules, with explainable AI techniques.
Outputs
Manuscript in preparation; no publication yet.

Code and research artifacts

Public repositories, described by what they actually contain.

  • G.H.O.S.T. simulation code and data

    Research artifact

    Python simulations and CSV results accompanying the ICISSP 2026 paper: entropy measurements, an intersection-attack experiment, modeled latency and saturation, communication overhead, and token economics.

    Simulation artifacts only. The repository does not contain a deployed messaging network or an Ethereum smart-contract implementation.

  • Authentication Module Lab

    Teaching example

    Educational authentication examples in Python and Java: registration, salted password hashing, login, logout and session handling, with a small Flask API, browser pages and unit test examples.

    Built for studying authentication design, not for production use. It hashes passwords with salted SHA-256, stores users in a local JSON file and keeps sessions in memory without expiry.

Grants and sponsored research

  1. 2022 – 2027

    Increasing Perseverance and Retention of Computing and Engineering Students Through Service

    National Science Foundation. Co-Principal Investigator. Education and student retention.

  2. 2021 – 2022

    Security Evaluation and Improvement of the Personal Cyberinfrastructure with New Tools and Education Development

    CRDF Global. Co-Principal Investigator. Security research and education.

  3. 2020 – 2021

    Self-Learning Capabilities for Mission-Oriented Data Quality and Security Assurance in Military IoT Systems

    U.S. Military Academy / Department of Defense. Co-Principal Investigator. Data quality and IoT security research.

Student mentoring

Teaching portfolio and mentoring

  • Undergraduate capstone projects
  • Independent and directed research
  • Graduate theses
  • Internships and cooperative studies
  • Cybersecurity practicum

Owen Weissman presented a privacy-messenger project at Sacred Heart's 2025 Academic Festival. That work fed into G.H.O.S.T., which was published at ICISSP 2026 with Owen as a coauthor.

Students interested in research in these areas are welcome to email me to talk about their interests.

Talks and service

  1. March 2026

    Session chair, Security Testing

    ICISSP 2026

  2. January 2025

    How AI Can Be Used to Enhance Your Cybersecurity

    BrightTALK webinar

  3. 2024 – 2025

    Faculty Presidential Seminar participant

    Sacred Heart University

  4. Ongoing

    Artificial Intelligence Committee

    Sacred Heart University, with curriculum and accreditation work

  5. Ongoing

    Public talks on cybersecurity and privacy

    Local libraries and media appearances

  6. March 2018

    Data Quality and Security Evaluation Framework, with Leon Reznik

    Trusted CI webinar

About

I joined the School of Computing & Engineering at Sacred Heart University in 2021. I received my Ph.D. in Computing and Information Sciences from Rochester Institute of Technology in 2020, where my dissertation developed an integrated framework for evaluating data quality and security on mobile devices.

As a postdoctoral research scientist at RIT, I worked on automated vulnerability intelligence: using machine learning and expert systems to curate and characterize vulnerability reports. Before my doctoral studies I built software for Android, Windows and embedded systems, including leading an embedded development team.

Academic and professional experience

  1. 2021 – present

    Assistant Professor of Cybersecurity

    Sacred Heart University, School of Computing & Engineering

  2. 2020 – 2021

    Postdoctoral Research Scientist

    Rochester Institute of Technology. Automated vulnerability intelligence

  3. 2016 – 2020

    Ph.D. student and research assistant

    Rochester Institute of Technology. Advisor: Dr. Leon Reznik

  4. 2013 – 2015

    Embedded team leader

    Dynamo Development. Android, Windows and embedded software

Education

  1. 2020

    Ph.D., Computing and Information Sciences

    Rochester Institute of Technology

  2. 2007

    Master's degree, Electronic Systems

    National Technical University of Ukraine “Igor Sikorsky Kyiv Polytechnic Institute”

  3. 2005

    Bachelor's degree, Electronic Systems

    National Technical University of Ukraine “Igor Sikorsky Kyiv Polytechnic Institute”

Outside work

Outside work I repair and build electronics, operate as a licensed GMRS radio user, bake pizza and cook over an open fire, and spend weekends hiking and camping around New England.

Contact

The quickest way to reach me is by email. You can also use the form, which sends a message to my inbox.

[email protected]

Profiles